A 20-minute read
Most boards receive cyber reports.
Few receive cyber evidence.
Are your board meetings governing cyber and AI risk — or simply receiving updates?R.J. MacEoin is the creator of PRISM Assure™ — the operating model for continuous cyber and AI assurance, built for boards, executives, and the risk professionals who support them.

Governing Cyber Risk in the AI Era
Cyber and AI risk are now board-level accountability issues. Yet many organisations still rely on retrospective reports, annual audits, and dashboards that show activity rather than assurance.
For Boards & Directors
A clearer way to govern cyber and AI risk — and build a defensible record that oversight was active, informed, and evidence-based.
For CISOs & Security Leaders
A structured assurance model built around control effectiveness, risk appetite, and evidence — not reporting theatre — and a way to connect cyber and AI security directly to business strategy in the language of boards and executives.
For Governance Practitioners
A way to move up the value chain as AI automates the compliance workflows their careers were built on.
 COMPLIMENTARY RESOURCES
The Board and Executive Guide to Continuous Cyber and AI Risk Assurance
A 20-minute read for boards and executives. Why point-in-time audits and certificates no longer prove that cyber and AI risk is under control, and the operating model that replaces them with continuous evidence.
- Why SOC 2, ISO 27001 and annual audits fall short of what boards now need
- The four-layer model, from board risk appetite to live control proof
- How to govern AI adoption, not just cyber risk
- “Red means decision” — what the board must decide when an indicator turns Red
- Eight questions for your executive team, and a 90-day plan to start
 COMPLIMENTARY RESOURCES
KPI-to-Control-Proof Catalog
The implementation layer for the PRISM Assure model — the workbench for practitioners, the specification for executives. Every indicator, cyber and AI alike, mapped down to the evidence that proves the control is working.
An Excel workbook, best opened on a computer.
- All 7+1 KRIs, with KPIs mapped to CIS Controls v8.1 and NIST SP 800-53
- OWASP GenAI Data Security 2026 mapping for the +1 AI indicator
- Control Proof formats — what evidence looks like, who produces it, how often
- Ownership guidance and board-ready threshold language
Two resources for governing cyber and AI risk
One for the boardroom, one for the people who have to produce the evidence behind it. Both cover cyber and AI in the same model.
We will email you both, then occasional notes on governing cyber and AI risk.
Register once. Access both and more for the future.
Live preview
Try the Catalog online before you download it
The Control Proof Explorer is a live preview of the KPI-to-Control-Proof Catalog. Select the platforms your organisation uses, and see which controls you can already prove and where the gaps are. When you want the full working version, sign up above.
Open the live preview
7+1
Key Risk Indicators
76
KPIs
256
Control Proofs
R.J. MacEoin’s aim is to give boards and executives an open, informed conversation about cyber and AI risk, and to free security teams to focus on what matters most: protecting the organisation.
Available now on Amazon — start building defensible cyber oversight today.

These resources give you the starting point. The book gives you the full operating model — why the chain from board intent to operational proof is missing in most organisations, and how to build it end to end for both cyber and AI risk.
Move beyond theory and implement a governance model that stands up to scrutiny: board-approved risk appetite, the 7+1 indicators, the KPIs beneath them, and the evidence that proves controls are working.
The AuthorGet in touch
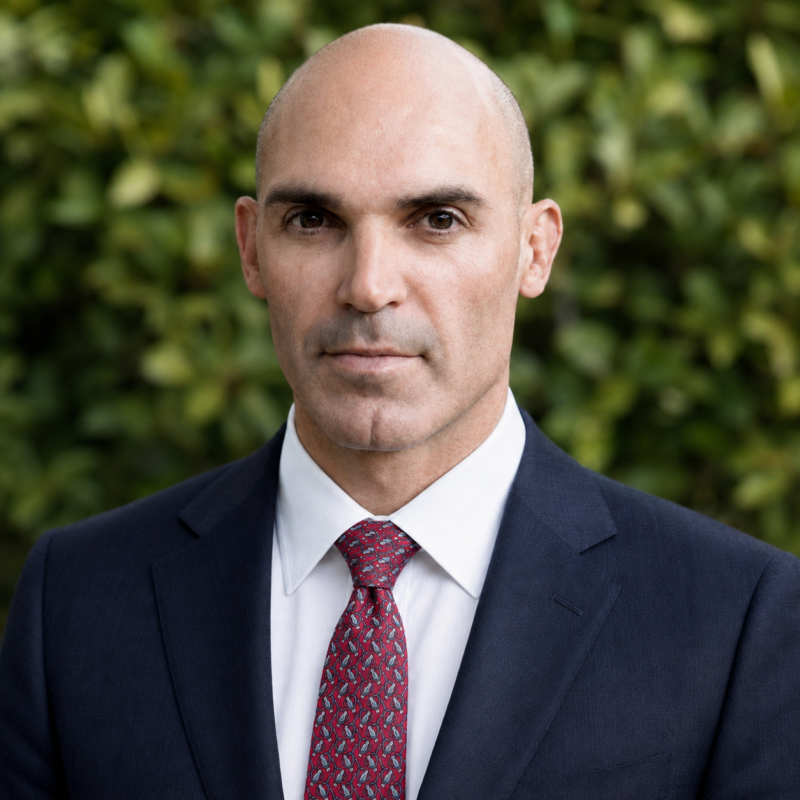
R.J. MacEoin
Commissioned through the Royal Military Academy Sandhurst, he served as Global Cyber Regulatory Lead for Western Union and Security Lead at Sumitomo Trust Funds Ltd, having earlier advised clients at PwC.
R.J. MacEoin holds the CISSP and GDSA, and advises boards across financial services, technology, and professional services on cyber governance and risk.